From traditional CSPM to a unified platform that prioritizes real risk
Cloud environments are becoming increasingly complex and, as a result, security teams have more and more information to analyze. Vulnerabilities, misconfigurations, threats or exposed resources generate multiple signals that, when analyzed in isolation, do not always reveal the real level of risk.
In this context, AWS positions AWS Security Hub as a solution designed to connect these signals and provide a more complete view of risk. Today, AWS Security Hub and AWS Security Hub CSPM are complementary services: CSPM focuses on assessing security posture, while Security Hub correlates that information with other signals to identify and prioritize the most relevant risks.
In short: Security Hub CSPM answers “Is it configured correctly?”; AWS Security Hub answers “Which risk needs the most attention?”. They don’t replace each other: they complement each other.
1. What is AWS Security Hub CSPM?
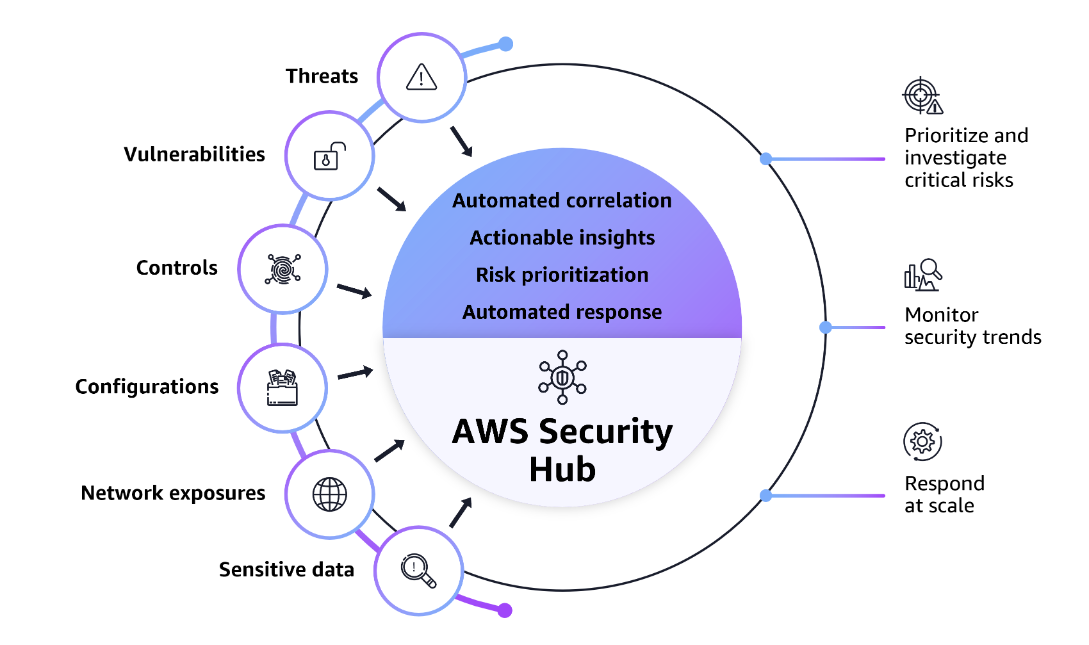
Security Hub CSPM (Cloud Security Posture Management) is the AWS service that assesses the security posture of an AWS environment. It runs automated checks against security configurations and best practices, making it possible to identify potential non-compliance and understand the security status of AWS accounts.
CSPM helps answer questions such as:
- Are there any misconfigurations?
- Are security best practices being followed?
- Which controls are failing?
- Which resources or accounts need attention?
In short, Security Hub CSPM shows the security posture of the environment. However, detecting a configuration issue is not always enough to determine the risk it represents across the infrastructure as a whole.
2. What is AWS Security Hub?
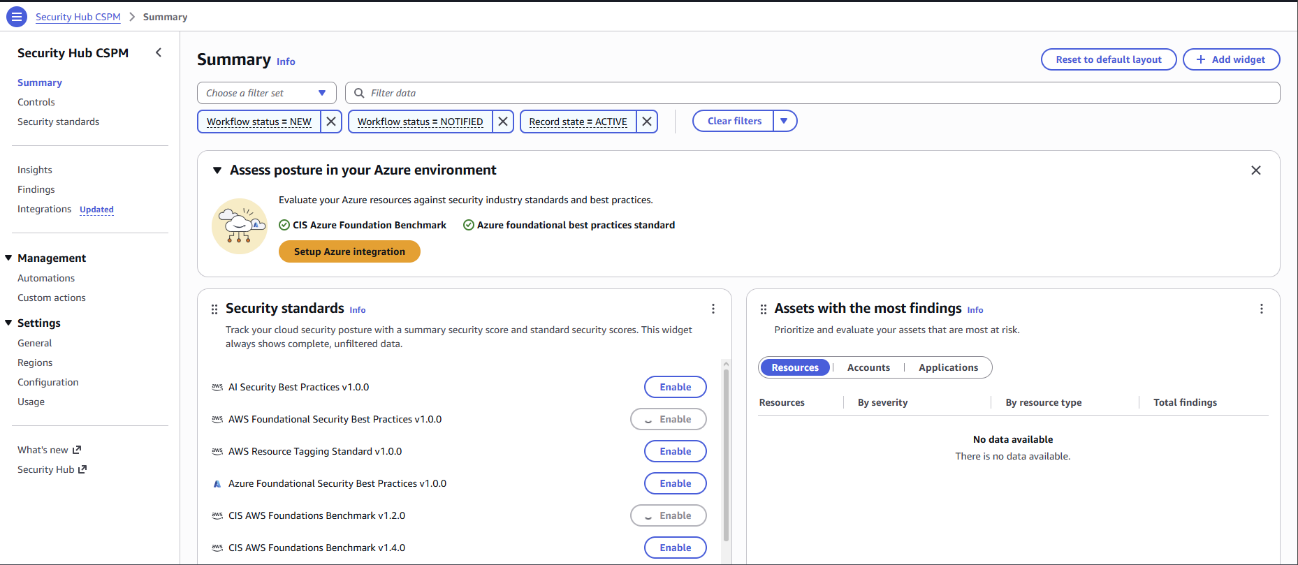
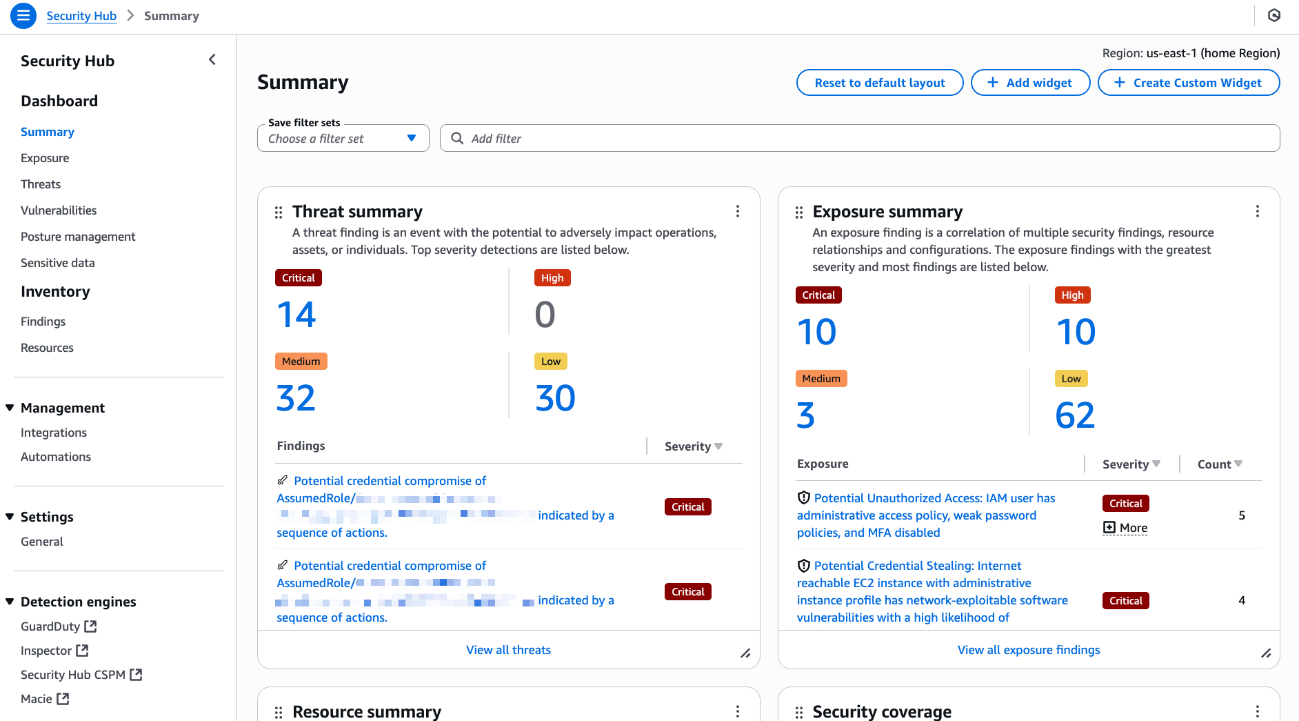
AWS Security Hub is the unified AWS platform that correlates signals from different security services to identify and prioritize the real risks in your environment. It extends the CSPM approach and adds context to every signal detected.
To do this, Security Hub works with information related to:
- Threats: from services such as
Amazon GuardDuty. - Vulnerabilities: identified by
Amazon Inspector. - Controls and configurations: from
Security Hub CSPM. - Sensitive data: linked to potential exposure risks.
- Network exposures: resources reachable from the Internet.
With Security Hub, the goal is not just to detect issues, but to understand how they relate to each other and what risk they pose to the environment.
3. Security Hub vs. Security Hub CSPM: key differences
Although both services are related, they serve different purposes. AWS presents them as complementary capabilities that, used together, provide a more complete view of the environment’s security.
| Security Hub CSPM | AWS Security Hub | |
|---|---|---|
| Goal | Manage security posture | Identify and prioritize risks |
| Focus | Configuration, controls and compliance | Correlation, context and risk analysis |
| Information | Security best practices and controls | Threats, vulnerabilities, configurations, exposures and other security data |
| Outcome | Posture findings | Contextualized risks and exposures |
| Key question | “Is it configured correctly?” | “Which risk needs the most attention?” |
4. Key capabilities of AWS Security Hub
One of the main features of AWS Security Hub is the ability to centralize different security signals and analyze them together.
Unified security view
Security Hub provides a centralized console to review threats, vulnerabilities, configurations and exposures, offering a combined view of security operations. All the information is available from a single place, giving you an overall picture of the environment.
Exposure analysis
Security Hub lets you analyze how different issues can combine and what impact they could have:
- Attack paths (
Attack Paths). They show how an attacker could chain vulnerabilities and misconfigurations to reach critical resources. Impact Analysis. It shows the resources that could be affected by an exposure and the potential privilege escalation paths within the environment.
Network Scanning: Internet-exposed resources
Network Scanning identifies the resources that are actually reachable from the Internet and detects exposed ports and services. AWS shows this capability for both AWS and Microsoft Azure resources, which is especially relevant in multicloud environments.
This way, the analysis no longer focuses only on whether a finding exists, but also considers which resources are affected, how they are related and what consequences a given exposure could have.
5. Conclusions
AWS Security Hub represents an evolution in how cloud environment security is approached:
- Security Hub CSPM continues to provide the posture view: controls, configurations and best practices.
- AWS Security Hub uses that information together with other signals to add context, correlate risks and make prioritization easier.
- The goal is not to have more findings, but to understand which issues represent real exposure.
Security is not just about knowing what is wrong, but about understanding what could happen and where action is needed.
Sources
- AWS Security Hub – official documentation (AWS Documentation)
- AWS Security Hub CSPM – official documentation (AWS Documentation)
- What are Security Hub and Security Hub CSPM? (AWS Documentation)
- General availability of Security Hub and risk analytics (Amazon Web Services)
How Aleson ITC helps you prioritize real risk in your cloud environment
Enabling Security Hub is the first step. What makes the difference is knowing how to interpret its findings, deciding what to fix first and keeping a consistent environment when AWS and Azure coexist.
At Aleson ITC, our Cloud Environment Security service helps you review permissions, reduce the exposure of your resources and turn alerts into a prioritized action plan.
Want to know the real risks in your cloud environment? Contact our team and we’ll help you assess them.
FAQ — Frequently asked questions about AWS Security Hub
What is the difference between AWS Security Hub and Security Hub CSPM? Security Hub CSPM assesses security posture (configurations, controls and compliance with best practices). AWS Security Hub correlates those findings with threats, vulnerabilities, sensitive data and network exposures to prioritize the risks that need the most attention.
Does AWS Security Hub replace Security Hub CSPM? No. AWS presents them as complementary services: CSPM provides the posture information, and Security Hub uses it, together with other signals, to add context and prioritize risks.
Which AWS services integrate with Security Hub? Among others, Amazon GuardDuty (threats), Amazon Inspector (vulnerabilities) and Security Hub CSPM (controls and configurations), as well as information on sensitive data and network exposures.
What are attack paths (Attack Paths) in AWS Security Hub? They are visualizations that show how an attacker could chain vulnerabilities and misconfigurations to reach critical resources, helping you decide what to fix first.
Can AWS Security Hub analyze Azure resources? Yes, in the case of Network Scanning: AWS shows this capability for identifying Internet-reachable resources and exposed ports in both AWS and Microsoft Azure. If you work in a multicloud environment, we can help you review it.